Compromise at scale
One signed update server is one door into every unit in the field. A device you cannot patch yourself, from a vendor you cannot reach, is an appliance you do not really own.
The attack surfaceBuilt here, for here
Sectech builds the security devices our market needs — starting with the software, moving to hardware we design ourselves, and hardware we will manufacture in Lebanon. No foreign cloud holding the keys. No subscription to keep the device alive.
The adoption gap
A decade of supply-chain exploits — hijacked update servers, backdoored cameras, firmware signed by nobody you can audit — has taught the market to hesitate. The technology is ready; the trust is not. And the gap is not going to close by importing harder.
One signed update server is one door into every unit in the field. A device you cannot patch yourself, from a vendor you cannot reach, is an appliance you do not really own.
The attack surfaceSome of our needs are simply not on any global vendor's roadmap — the market is too small to be worth their support, so the need stays unmet. That is a gap local engineering can close and only local engineering can close.
The coverage gapDevices get sold and abandoned. When the vendor, the installer and the distributor are all gone, there is nobody left who can patch it, repair it, or answer the phone.
The ownership gapYou cannot import your way out of this. Somebody has to build it here.
What we build
Some problems exist because nobody local solved them. Others exist because nobody could be trusted to. We take both kinds.
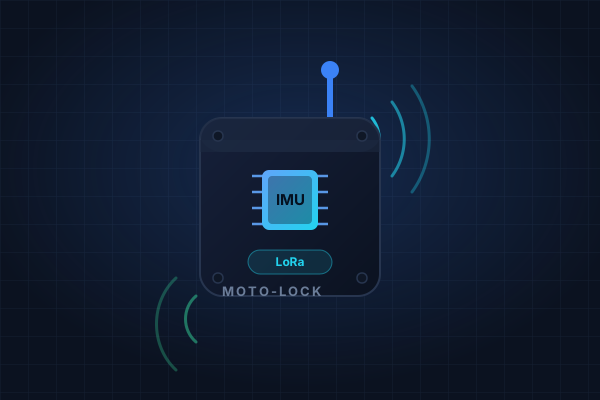
A motorcycle parked in Beirut is a specific problem — theft patterns, vibration profiles, concrete garages with no signal, and a market no global alarm maker will build a product for. We build for this exact problem, not around it.
When we ship it, we ship the source, the update path and the patch. You can read what runs on your device, you can verify it, and you can reach someone who can change it.
Products
One is a sensor problem we had to solve ourselves. The other is a trust problem we had to solve ourselves. Both run without a vendor cloud.
A motorcycle alarm that tells a passing truck from a thief, reaches across a parking structure without a cellular subscription, and stays under $35 at the base kit.
Self-hosted AI video security: licence-plate reading, intrusion detection, footage search and a camera agent that answers questions — running on a box at your site, with no cloud and no monthly fee.
Manufacturing roadmap
Every step moves the same value closer to us — and closer to you. We do not skip steps, and we do not pretend to be further along than we are.
We write all the firmware and applications ourselves, on off-the-shelf components we can source, inspect, replace and stop depending on. Fast to ship, no single vendor roadmap in control.
In progressOur own boards, enclosures and radio stack — specified here, drawn here, manufactured by a partner we can hold to a specification we wrote.
In designLocal assembly and manufacture. Short supply lines, local accountability, faster repair cycles, and more of the value staying in the country.
On the roadmapSecurity patches, firmware updates, after-sales support and hardware upgrades for every product we have ever sold — not just the current one.
CommittedAfter-sales
The cheapest device in the world is worthless if nobody answers when it fails. We treat the years after the sale as part of the product.
When a vulnerability is disclosed in a component we use, we ship a firmware update. We hold the signing keys, so we do not wait on anyone else to do it.
Same timezone, same language, people who can actually open the device. No ticket queue on another continent.
We design for serviceability and keep spares for the products we ship. A working device should be repaired, not thrown away.
Software upgrades land on hardware already in the field — a customer with a working installation is never asked to pay twice for the same capability.
Every product carries a stated support window and a minimum security-update commitment per release line, so you can plan instead of guessing.
No remote kill switch, no deactivation server, no licence check that decides whether your hardware is still allowed to work.
Why local matters
We cannot promise a world without supply-chain attacks. We can promise who is holding the pieces, who can change them, and who you call when they need changing.
We write the firmware and the applications. Where we can publish it, we do — so a third party can audit what is running on your device.
We sign our own firmware. A compromise at a foreign update server does not reach your unit, because your unit never talks to that server.
No vendor cloud, no third-party analytics, no telemetry you did not agree to. The device works with the network unplugged.
The engineer who answers is the engineer who wrote the code. Nothing is escalated to a support queue somewhere else.
As we move from bought components to our own boards and local manufacture, the bill of materials becomes something we control rather than something we hope about.
No remote kill switch, no deactivation server, no licence check that decides whether your hardware is still allowed to work.
Work with us
We are early and we are building in public. If you need a device that does not exist yet, if you want to distribute or install what we make, or if you want to back the company — start the conversation.
Product enquiries, pilot sites and distribution — all start in the same place.